
AlmaLinux 10: SELinux booleans are switches, not permissions
Test scope
Section titled “Test scope”An AlmaLinux 10.2 Server VM, SELinux Enforcing, policycoreutils-python-utils 3.10.
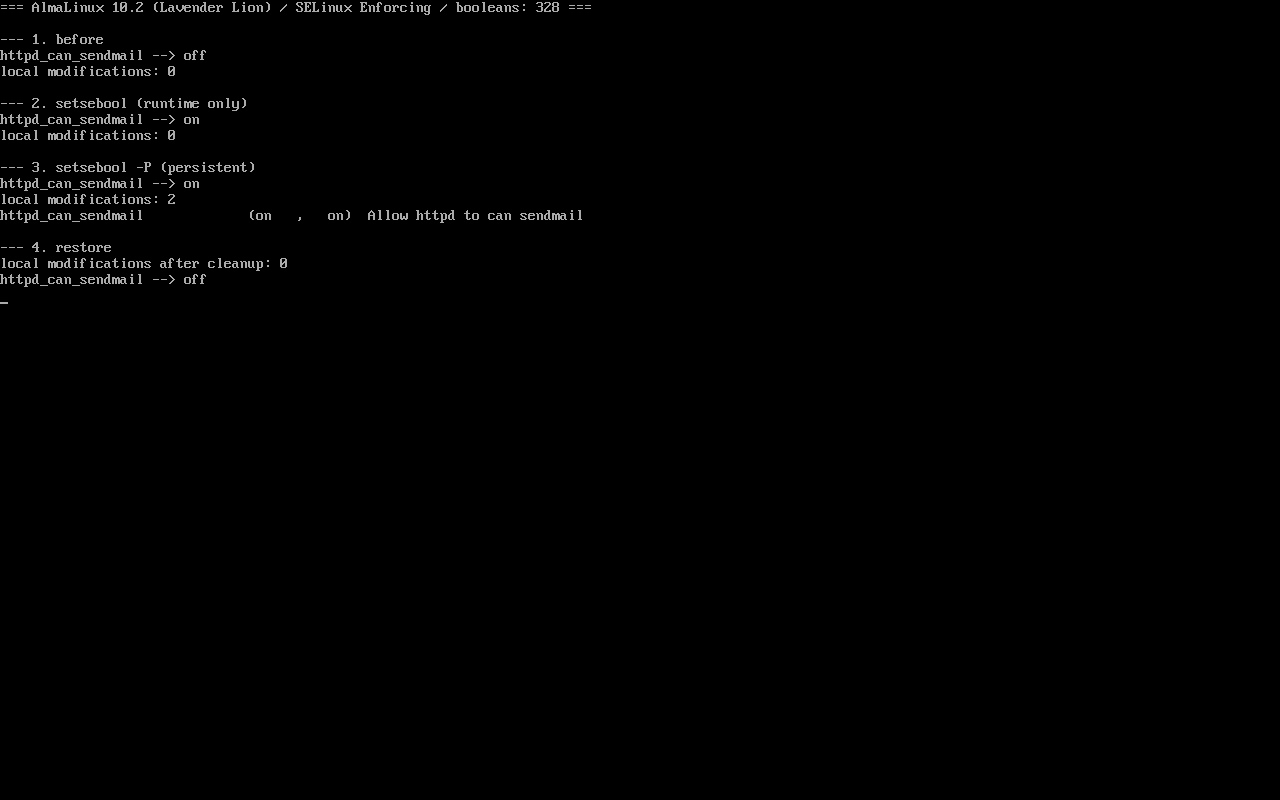
Verified: enumerating booleans, runtime toggle, persistent toggle, inspecting local customizations, cleanup. Screenshot: public/evidence/selinux/alma-booleans.png.
How many booleans exist
Section titled “How many booleans exist”$ getsebool -a | wc -l328All 328 are switches the policy exposes. getsebool -a prints only names and values; for descriptions and defaults use semanage boolean -l:
$ semanage boolean -l | grep -E "^httpd_can_sendmail "httpd_can_sendmail (off , off) Allow httpd to can sendmailThe pair is “current, default”. The default comes from the policy; your change is only a local override.
The difference between setsebool and setsebool -P is measurable
Section titled “The difference between setsebool and setsebool -P is measurable”$ setsebool httpd_can_sendmail on$ getsebool httpd_can_sendmailhttpd_can_sendmail --> on$ semanage boolean -l -C | tail -n +2 | wc -l0The value changed but the override count did not — setsebool only affects the running policy and is lost on reload or reboot.
$ setsebool -P httpd_can_sendmail on$ semanage boolean -l -C | tail -n +2 | wc -l2$ semanage boolean -l -C | grep "^httpd_can_sendmail"httpd_can_sendmail (on , on) Allow httpd to can sendmailOnly -P writes to the policy store. semanage boolean -l -C lists local customizations and is the authoritative check for persistence.
Where the override lives
Section titled “Where the override lives”$ ls /var/lib/selinux/targeted/active/booleans.local/var/lib/selinux/targeted/active/booleans.localThe /etc/selinux/targeted/active/ path found in older docs no longer exists in the modern policy store.
A switch, not a permission
Section titled “A switch, not a permission”A boolean does not create access; it selects between rules already compiled into the policy:
| What people assume | Reality |
|---|---|
Enabling httpd_can_network_connect opens any port | It lets the httpd domain initiate connections; target ports still follow policy |
| Turning a boolean off hardens the host | It may break a service and leaves the real attack surface intact |
The correct order is: read the AVC denial, identify the rule, then decide between a boolean and a label/port fix.
$ ausearch -m AVC -ts recent | tail -5audit2why translates denials into plain language; sesearch requires setools-console, which neither minimal nor Server installs.
Clearing overrides
Section titled “Clearing overrides”$ semanage boolean -D$ semanage boolean -l -C | tail -n +2 | wc -l0-D removes all boolean customizations, not one. On a shared host, run semanage boolean -l -C first so you do not wipe someone else’s tuning.
Common traps
Section titled “Common traps”setseboolthen reboot: gone, because-Pwas missing;-Cshows 0 but the value is not default: that is a runtime-only change;- Using booleans as a firewall: reachability belongs to firewalld;
- Treating
-Das “delete one”: it clears everything.
Practice: a full round trip
Section titled “Practice: a full round trip”sudo semanage boolean -l | grep -i nis | head -3sudo getsebool -a | grep nis | head -3sudo setsebool <chosen> onsudo semanage boolean -l -C | tail -n +2 | wc -l # still baselinesudo setsebool -P <chosen> onsudo semanage boolean -l -C | tail -n +2 | wc -l # baseline + 1sudo setsebool -P <chosen> offsudo semanage boolean -DChecks:
- The count grows only after
-P; -Dreturns it to zero;- The boolean returns to the policy default;
- No service was affected (this example is not tied to one).
常见问题
Boolean or file context first?
Follow the AVC: if the path label is wrong, fix the label (restorecon/semanage fcontext). Only when labels are right and policy still blocks should you consider a boolean.
Can I define my own booleans?
Yes, by declaring gen_bool in a custom policy module — that is policy development, not an ops toggle.
Why does a changed boolean have no effect?
The service may not have reloaded policy, or the boolean only affects a code path that is not used; restart the service and re-test.
Next steps
Section titled “Next steps”- Labels and contexts: /en/selinux-basics/
- Hardening: /en/hardening/
- Logs: /en/journald-logging/